

Joining the Platform
Access to Prisme.ai is two-staged: a user must first have an account on the platform, and then become a member of one or more organizations. Platform access is the prerequisite; without it, organization invites and links cannot be redeemed. A platform account is created in one of two ways:- Local signup: the user signs up with an email and password. Local signup must be enabled at the platform level, and depending on configuration, new accounts may require superadmin validation before they become active.
- SSO login: the user authenticates through a configured identity provider (OIDC or SAML). The account is created automatically on first login. If the SSO provider is attached to an organization, the user is also added to that organization (see SSO auto-join).
Joining an Organization
Once a user has a platform account, they can become a member of one or more organizations. Prisme.ai offers four distinct mechanisms, each with different trade-offs:When to use each mechanism
- Email invite: invite a specific person who may not yet have an account. The invitation prepares their membership with the right role; they automatically join the organization on their first login, whether through local signup or SSO.
- Invitation code (link): share a single link with a group of people so they can join the organization on their own with the right role. Invitation codes only work for users who already have a platform account. You can monitor the usage count and revoke a link at any time.
- Join rules: automatically grant organization membership based on user attributes (email domain, SSO claims, custom metadata). Best when membership should be governed by conditions you control rather than per-user actions.
- SSO auto-join: use when an organization has its own SSO provider; everyone authenticating via that provider becomes a member. Combine with join rules to assign granular roles or groups.
Sharing an invitation link with someone who isn’t on the platform yet? Invitation links require the recipient to be authenticated. Either send them an email invite (which works without a pre-existing account), or ask them to sign up first (local signup or SSO) before clicking the link.
Creating an Organization
A guided setup creates an organization and makes it usable in a few minutes: its name and logo, its colors, the apps in its menu and who joins it automatically.Who can create an organization
Self-service creation is a platform-level setting (self-hosted deployments set it as an environment variable of the API gateway):
Anonymous sessions can never create an organization. Setting
ORGS_MAX_PER_CREATOR to 0 removes the limit. The person who creates an organization becomes its Owner.
The guided setup
Users allowed to create an organization can start it from the organization switcher, on the welcome screen shown to a user who belongs to no organization yet, or from AI Governance > Organizations. The setup runs in four steps, with a live preview of the result:- Identity: the organization name, its identifier (used in URLs) and its logo.
- Appearance: a color palette, suggested from the logo or picked from presets.
- Use cases: the apps that make up the menu of the organization (chat, agents, knowledge, governance and so on).
- Access: an optional join rule on the creator’s own email domain, with the role new members receive. When the creator’s current organization already has allowed AI models, the setup offers to reuse them.
If a part of the setup cannot be applied (for example a join rule the platform refuses), the organization is still created and the final screen offers to retry that part only.
Inviting Members
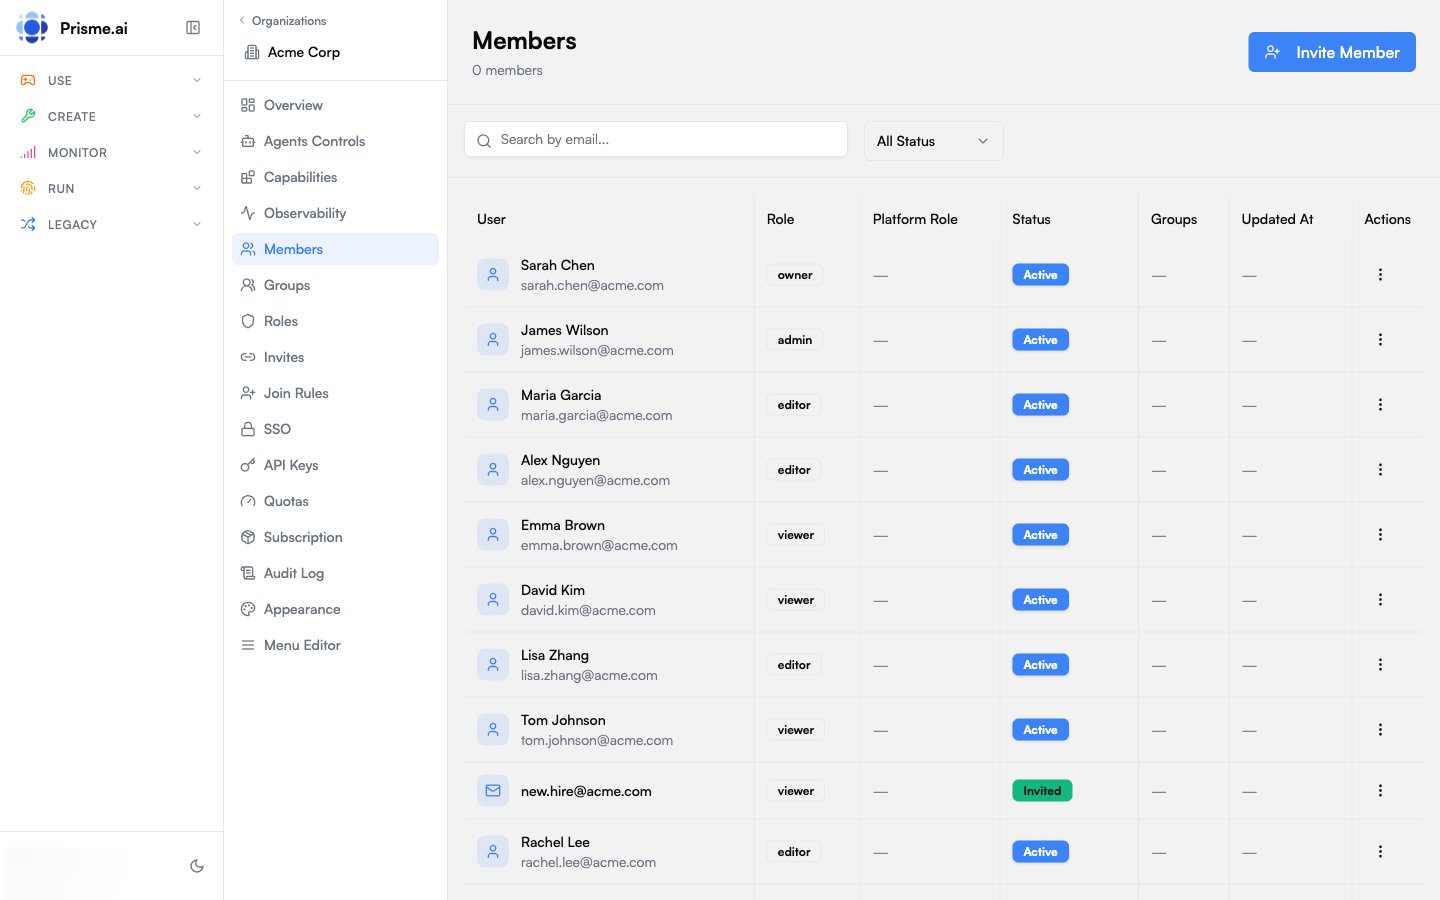
To invite a specific user by email:- Go to Members in the sidebar
- Click Invite Member
- Start typing a name or an email address. The field autocompletes against the platform’s users, so an existing account can be picked from the list instead of being retyped
- Select a role to assign
For sharing access with multiple people at once via a reusable link, use Invitation Codes instead.
Managing Existing Members
From the Members list, you can:- Change role: click a member and select a new role
- Suspend: temporarily disable access without removing membership
- Remove: permanently remove the user from the organization
Join Rules
Join rules allow automatic organization membership based on user attributes. When a user joins through a rule, they receive the rule’s role and group memberships.Rule Structure
Each join rule contains an array of conditions with AND logic (all conditions in a rule must match):Rule order matters. Rules are evaluated in order and the first matching rule wins: its
role and groups are applied, and any subsequent rules that would also match are ignored. Reorder rules from the Join Rules screen to control precedence (e.g. put more specific rules above broader catch-all ones).Condition Fields
Creating a Join Rule
- Go to Join Rules in the sidebar
- Click Add Rule
- Define conditions
- Select the role to assign
- Optionally select groups to add the user to
Who can add which rules
A join rule makes every matching user a member at their next login, so an unrestricted rule would let any organization owner pull a whole company into an organization they control. Outside platform administrators, a rule that is added or changed must therefore:- Target the author’s own company. One condition of the rule must be anchored on the identity of the person saving it:
emailendsWiththeir own email domain (@acme.com),emailequalsan address of that domain, or their own SSO tenant (authData.azure.tidorauthData.google.hdequalstheir value). The other conditions are combined with AND, so they can only narrow the rule. Public mailbox domains (gmail.com, outlook.com and the like) are never accepted. - Name the role it grants. A rule without a role is refused: the role members receive is the one written in the rule.
- Grant a role that does not manage the organization. Owner, Admin and any custom role holding
*or anorgs:...:managepermission cannot be granted to a whole domain.
Importing and exporting rules
The Join Rules tab reads and writes its whole ruleset as JSON. Export downloads the current rules, Import applies a file to the organization. The same import and export exists on Agents Controls and, with a multiselect, on Capabilities, so a governance setup validated in one organization or environment can be replayed in another instead of being re-entered rule by rule.Rule Evaluation
Join rules are evaluated on every/me API call (the first call the platform makes after authentication). A per-user version cache ensures rules are only re-evaluated when they change:
- Each org’s join rules have a version counter (incremented when rules are updated)
- The gateway tracks which version was last evaluated for each user
- If the version matches, evaluation is skipped for that org
Join rules grant membership; they do not keep it in sync. A user who is already a member of the organization is skipped, whatever way they joined. Their role and groups stay as they were, even if their SSO attributes changed since (for example after being added to an identity-provider group). To change an existing member’s access, change their role from the Members list, or re-evaluate the rules on the existing members. For a rule to set the role on arrival, make sure the user’s attributes are in place before their first login to the organization.
Re-evaluation on Rule Changes
When an organization’s join rules are updated, the platform re-evaluates all existing members who joined via join rules:- Members who no longer match any rule are automatically removed from the organization
- New users who now match are not retroactively added; they join on their next
/mecall, unless you apply the rules right away (see below) - Re-evaluation processes members in batches of 500
existingMembers: "all" also evaluates them, only to update their role and groups.
For a member who joined through a join rule, a rule change has two possible outcomes:
A rule change on its own only assigns a rule’s
role and groups when the user joins the organization. To bring existing members in line with a new ruleset, re-evaluate the rules with the existingMembers option, or update them from the Members and Groups screens.Simulating and applying rules
Before saving a ruleset, you can measure its impact withPOST /v2/orgs/{orgSlug}/join-rules/apply. It requires the orgs:join-rules:manage permission and runs as a dry run by default: nothing is written.
From the interface, the Re-evaluate button of the Join Rules screen runs it on the saved rules: the simulation is checked by default and lists the members to remove, the members to update and the users who would join. Unchecking it starts the apply in the background. Saving the rules already removes the members who no longer match them (see Re-evaluation on Rule Changes): on saved rules, the members to remove are only those whose attributes changed since, for example an SSO claim.
The dry run response reports:
rulesDiff: rules added, removed or moved compared to the current rulesetshadowedRules: rules that can never apply because an earlier rule already matches every user they would match, for example a short prefix placed above a longer onemembers: current members who joined through a join rule and would be removedjoiners: users who are not members yet and would join, with the number per rule and, for each listed user, the rule that matches first, the role and the groups they would get. Anonymous, pending and deactivated users are ignored.updates(withexistingMembersother thannone): current members whose role or groups would change, with the number per rule and, for each listed member, the rule that matches first, the role change (from,to) and the groups added and removed.skippedcounts the members who would have changed but manage the members or the join rules.
A platform administrator acts on every platform user. An organization administrator only acts on users who belong to no organization yet, counts included. Users of other organizations who match the rules still join at their next login, as with any join rule. For organization administrators, the endpoint is also rate limited (
RATE_LIMIT_JOIN_RULES_APPLY calls per minute, 5 by default)."dryRun": false, the candidate rules are saved and the response comes back right away with applied.status: "started". The apply then runs in the background: it removes the members who no longer match, updates the existing members in the existingMembers scope, then adds every matching user without waiting for their next login. Its outcome (members removed, members updated, users added in total and per rule, failures) is recorded in the organization’s audit log as join_rules_applied. Dry runs are recorded too, as join_rules_simulated.
Only one apply runs at a time per organization: a second call meanwhile is refused with a 409. Calling it again afterwards is safe, since users who are already members are skipped. An apply interrupted by a restart is therefore completed by a new call.
Updating existing members
By default, applying the rules never changes the members already in the organization, other than removing the ones who joined through a join rule and no longer match. WithexistingMembers set to join-rule or all, each member in that scope who matches a rule is brought in line with the first rule they match, as a new member would be:
Members whose role can change the members or the join rules (any permission granting it, such as
*, orgs:*, orgs:members:manage, orgs:members:update or orgs:join-rules:manage, which includes owners and administrators) are never updated: they are only counted in skipped, as are members whose role changed while the apply was running. Members added by an administrator, an invitation or SSO auto-join are never removed, even with all. The member keeps the way they joined: a member who joined through a join rule can still be removed by a later rule change.
Invitation Codes
Invitation codes let you share a link that grants access to your organization to anyone who already has a Prisme.ai account.Creating an Invite
- Go to Invites in the sidebar
- Click Generate Invite
-
Configure:
- Role: What role invitees receive
- Max Uses: Limit how many times the code can be used (optional)
- Expiration: When the code expires (optional)
- Share the generated link
Recipients must be authenticated on the platform to redeem an invitation link. If a recipient does not have a platform account yet, use an email invite instead, or ask them to sign up first (local signup or SSO).
Invite Status
Roles & Permissions
Roles define what actions members can perform. Each role contains a set of permissions.For the big picture (how organization roles combine with super-admins and workspace roles to authorize every action on the platform), see Self-Hosting → Permissions Management.
Permission Format
Permissions follow a hierarchicalproduct:resource:action pattern with wildcard support:
Wildcards are supported at any level:
orgs:members:* grants all member actions, storage:* grants all storage permissions, * grants everything.
agent-factory:traces:read gates reading an answer’s execution trace — the prompts, retrieved content and payloads a turn exchanged. It lives in its own traces resource, deliberately separate from the agent-editing permissions: someone allowed to change an agent is not thereby allowed to read its traffic. It is therefore not covered by the agent-factory:agents:* wildcard — it must be granted on purpose. Organization Owners hold it through *, and it is granted to Admins by default.agent-factory:sharing:cross-org gates sharing an agent beyond its own organization — with a specific other organization the sharer belongs to, or with all authenticated users (“All”). Same pattern as traces:read: its own sharing resource, not covered by agent-factory:agents:*, so editing agents never silently implies exposing them outside the organization. Owners hold it through *, Admins through agent-factory:*; every other role must receive it explicitly in the role editor (“Share Agents Across Organizations”).The
apikeys resource of each product (agent-factory, storage, ai-collection-v3) controls the API keys of its agents, knowledge bases or collections, on top of the share permission on that resource, resource owner included:Like
traces:read, apikeys is its own resource, not covered by agent-factory:agents:*: an administrator can let a role share agents without letting it manage keys that bill the organization. Owners hold it through *, Admins through their product wildcards, and the Agent Maker and Builder roles receive agent-factory:apikeys:* (they already hold storage:*). Keep delete wherever keys can be created, so a leaked key can always be revoked.llm-gateway:models:audio-transcriptions lets a member use speech-to-text, which powers chat dictation. The system Member, Agent Maker and Builder roles grant it by default. When the platform or the organization has a transcription model, remove it from a role to turn dictation off for its holders, in every browser. When there is no transcription model at all, it is not checked: desktop Chrome and Edge dictate with the browser’s own speech service, unless the fallback is turned off. See Dictate a message → For administrators. Which transcription model they can use still follows the organization’s allowed models.
Resource Scopes
Scopes restrict which specific resources a role can access, independent of permissions. They use the formatproduct:resource:id:
*grants access to all resourcesagent-factory:agents:*grants access to all agents- Empty or omitted scopes mean no resources are accessible
Per-resource sharing
Beyond the scopes hardcoded on a role, every resource instantiated by an Agent Creator or Knowledge project carries its own RBAC. From a project’s Share dialog, you can grant access to specific users or groups on that one resource, picking a product-managed role (e.g. Viewer / Editor / Owner). Those product roles map to the sameproduct:resource:action permissions used by organization roles.
This lets you give fine-grained access to a single agent or knowledge base even when the user’s organization role has no scope for that resource.
Built-in Roles
Organizations come with system roles that cannot be deleted:Reading roles and managing them are two different permissions. Every member carries
orgs:roles:read, which is what the Governe interface needs to load the roles list, so an Admin missing it used to be locked out of Governe entirely. Creating, updating or deleting an organization role requires orgs:roles:manage: being able to read the roles never implies being able to rewrite them.owner can be customized per organization. When an admin edits a system role in the Governe UI, a custom role override is saved for that organization that fully replaces the system definition.
Creating Custom Roles
- Go to Roles in the sidebar
- Click Create Role
- Enter name and description
- Select permissions using the Permission Tree Editor
- Checking a product node sets the product-level wildcard (e.g.
storage:*) - Checking a resource node sets the resource-level wildcard (e.g.
storage:vector_stores:*) - Individual actions can be toggled independently
- For products supporting instance scoping, a Scopes section appears under each resource, allowing admins to set the “All resources” wildcard or add specific resource IDs
Groups
Groups organize members for easier bulk management. Use cases include:- Department-based access (Engineering, Marketing)
- Project teams with shared permissions
- Geographic regions
Creating Groups
- Go to Groups in the sidebar
- Click Create Group
- Enter name, slug, and optional description
- Add members to the group
Using Groups with Join Rules
Groups work with Join Rules to automatically add new users to the right groups based on their attributes.SSO Configuration
Configure Single Sign-On with your corporate identity provider.The provider config format (OIDC / SAML,
attributesMapping, claims, certificates, …) is identical to the platform-level SSO documented under Self-Hosting → Authentication & SSO. The only difference is where you declare it: a Kubernetes ConfigMap for platform-wide SSO vs the Governance UI here for per-organization SSO. Refer to the self-hosting page for the full field-by-field reference and IdP-specific tips (Google Workspace, Okta, Auth0, Keycloak, ADFS, OneLogin, …).Platform SSO vs Organization SSO
Supported Providers
SSO Config Structure
SSO configuration is stored as part of the organization object (ssoConfig field):
Adding an OIDC Provider
- Go to SSO in the sidebar
- Click Add Provider
- Select OIDC
- Enter configuration:
- Configure attribute mapping to map IdP claims to user fields
- Optionally restrict to specific domains (e.g.,
@acme.com) - Enable the provider
Additional Configuration (JSON)
The form covers the fields most providers need. Any other OIDC setting goes in the Additional Configuration (JSON) section at the bottom of the provider dialog: paste a JSON object there and it is merged into the provider configuration. The most frequent use isuserinfo_endpoint. Some identity providers issue a minimal
token and keep the profile attributes (first name, last name, …) on their /userinfo
endpoint instead. The symptom is recognisable: users sign in successfully, but appear
without a name in the members list. To fix it, paste:
Existing members do not need to be removed and re-invited: their name and email are
refreshed from the identity provider at every sign-in, so the values appear at their next
login.
userinfo_endpoint must be an https:// URL, and your IdP must return an access token
alongside the identity token (standard OIDC behaviour). If the endpoint is slow or
unavailable, sign-in still succeeds and the user is simply created without the missing
attributes. See Reading profile claims from the userinfo endpoint
for the full behaviour and the complete list of settings accepted here.Adding a SAML Provider
- Go to SSO in the sidebar
- Click Add Provider
- Select SAML
- Enter configuration:
- If your IdP requires signed requests, enable Sign Authentication Requests (see below)
- Save, reopen the provider and click Download SP Metadata to configure your IdP
- Enable the provider
Signing authentication requests
When your IdP metadata containsWantAuthnRequestsSigned="true", the IdP rejects any authentication request that Prisme.ai does not sign. Enable Sign Authentication Requests on the provider and save:
- A 2048-bit RSA key pair and a self-signed certificate (valid 10 years) are generated and stored in the provider configuration. Requests are signed with RSA-SHA256, with a SHA-256 digest.
- The private key is never displayed nor returned by the API. Saving the provider again keeps it.
- The provider dialog shows the certificate and its expiration date. Register it on your IdP, or send it the service provider metadata (Download SP Metadata), which includes it and declares
AuthnRequestsSigned="true". The metadata is also available athttps://API_URL/v2/login/saml/<provider-slug>/metadata. - Turning the toggle off stops signing but keeps the key: turning it back on reuses the same certificate.
- Regenerate Certificate replaces the key pair immediately and is recorded in the audit log. Sign-in through the provider fails until the new certificate is registered on the IdP, so coordinate the rotation with its administrator.
privateKey and publicCert (PEM) together with signAuthnRequests: true in a PUT /v2/orgs/{orgSlug}/auth/sso/{slug} request: they must match, otherwise the save is rejected. The Additional Configuration (JSON) section only works for this on a provider that has no certificate yet, since the form keeps sending the stored one. See Signing authentication requests for the full field reference.
Request binding
Request Binding sets how the browser carries the authentication request to the IdP:- HTTP-POST (form submission), the default: the request is submitted to the IdP in a form.
- HTTP-Redirect (request in the URL): the browser is redirected to the IdP with the request in the URL.
400 such as “Request contains insufficient information to determine the protocol binding” while the browser shows a GET to the IdP without SAMLRequest: a proxy in front of the IdP is then likely losing the form submission. Save the provider for the change to apply.
With HTTP-Redirect, Skip Request Compression is turned off and disabled: the standard requires redirected requests to be compressed.
Changing the binding of a saved provider keeps its Entry Point URL, and the form shows a warning. If the IdP declares a different SSO URL for each binding, empty the Entry Point URL field and paste the IdP metadata again so that the URL matching the binding is used. See Request binding.
Domain Validation
When updating SSO config, the system validates that domains are not already claimed by another organization. If a domain conflict is found, the update is rejected with aDOMAIN_ALREADY_USED error.
Secrets Encryption
SSO provider secrets (OIDCclientSecret, SAML certificates) are encrypted at rest using envelope encryption (@prisme.ai/secrets) when the SECRETS_MASTER_KEYS environment variable is configured:
- A per-organization Data Encryption Key (DEK) encrypts the SSO config
- The DEK is wrapped by a platform-level Key Encryption Key (KEK) using AES-256-GCM
- Wrapped DEKs are stored in MongoDB alongside the org; plaintext secrets are never persisted
SECRETS_MASTER_KEYS is not configured, SSO configs are stored in plaintext.
API Keys
API keys (iak_*) enable programmatic access to the Prisme.ai platform from external systems. They are scoped to an organization and carry specific permissions and resource scopes.
Key Format
All API keys use the formatiak_{orgSlug}_{uuid}:
orgSlug allows the auth middleware to resolve the organization without a database lookup. Keys are stored hashed; the plaintext key is returned only once at creation time.
Creating an API Key
- Go to API Keys in the sidebar
- Click Create API Key
- Enter a name
- Select permissions using the Permission Tree (same
product:resource:actionformat as roles) - Optionally set scopes to restrict to specific resources (e.g.,
agent-factory:agents:agent-abc-123) - Set an expiration date if needed
Scopes
Scopes restrict which resources a key can access, even if the permission allows the action. They use the sameproduct:resource:id format as role scopes:
agent-factory:agents:* grants access to all agents, * grants access to all resources.
Using API Keys
Include the key in thex-prismeai-api-key header:
How API Key Validation Works
API key validation is handled natively by the platform runtime. When a request includes aniak_* key, the runtime resolves the organization, permissions, and scopes, then injects them into the standard run.permissions and run.scopes variables, the same variables used for user session auth. No cross-workspace HTTP call is needed.
Rotating Keys
- Click on an API key
- Click Rotate
- A new key is generated with zero downtime; the old key is immediately invalidated
Service Accounts
Service accounts are non-human identities for machine-to-machine authentication. They are also the mechanism behind the platform’s core principle that every agent is a service account with its own role, model, and tool restrictions. Use them for:- CI/CD pipelines
- Backend integrations
- Automated workflows
- Scheduled tasks
Creating a Service Account
- Go to Agents Controls > Service Accounts
- Click Create Service Account
-
Enter:
- Slug: URL-safe identifier
- Name: Display name
- Role: Permission set to assign
- Copy the generated client secret
Authenticating as a Service Account
Exchange the client credentials for an access token:Managing Service Accounts
- Enable/Disable: Toggle access without deleting
- View Last Used: See when the account last authenticated
- Rotate Secret: Generate a new client secret
Best Practices
Least Privilege
Grant only the minimum permissions needed for each role
Use Groups
Organize members into groups for easier permission management
Rotate Credentials
Regularly rotate API keys and service account secrets
Audit Access
Review audit logs to monitor permission changes
Join Rules
Automate onboarding with join rules for consistent access
Expire Invites
Set expiration dates on invitation codes